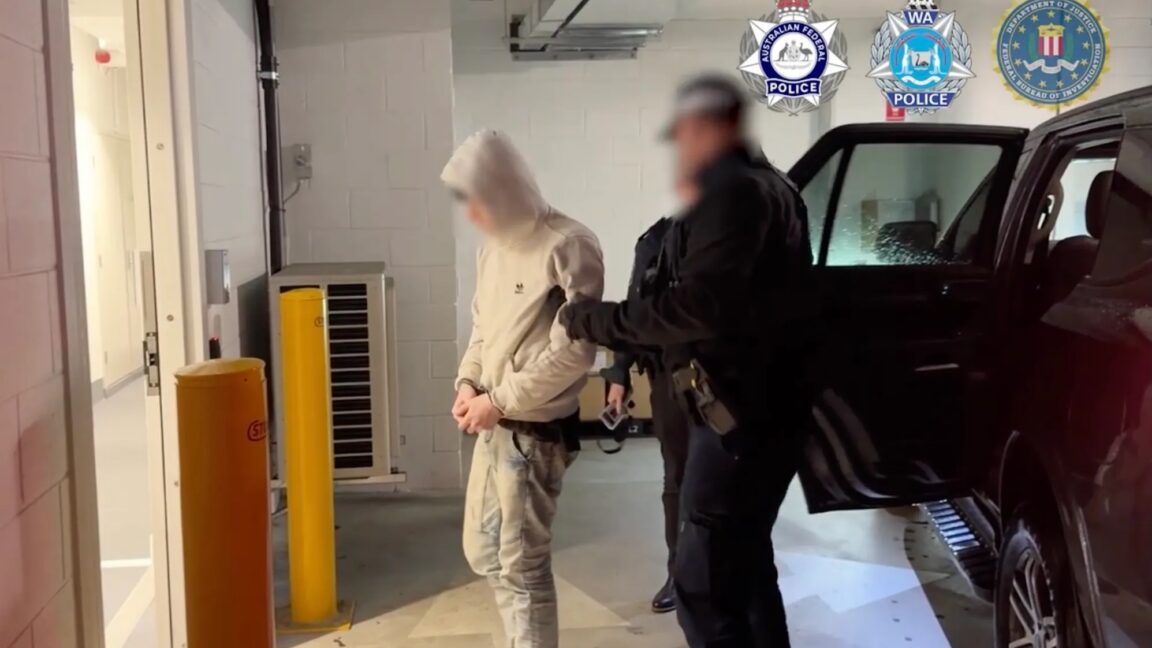
Authorities arrest 2 alleged members of prolific hacking group TeamPCP
The group infected more than 1,000 organizations in a relentless supply-chain attack campaign.
The group infected more than 1,000 organizations in a relentless supply-chain attack campaign.
The short version
- TeamPCP has vexed law enforcement officials and security personnel around the world since it emerged in December.
- The group is best known for a sustained series of supply-chain attacks that laced open source software with malware that self-propagated from one package to another.
- The viral infections worked by targeting organizations’ CI/CD pipelines, which are used to rapidly develop, update, and deploy software.
What happened
Once a package or tool was compromised, Shai-Hulud , as the worm was dubbed, attached itself to future package updates. When developers downloaded the compromised packages and ran them through their own CI/CD platforms, their software was also compromised.
Why it matters
Key to Shai-Hulud’s viral ability was a separate component that collected credentials for other packages in the memory of infected hardware.
Summary by Nerd News Network. Read the full article at Ars Technica via the links above and below.