Highlights from Splunk .conf26 and what the news means to network engineers
For network engineers, the main takeaway from the Sept.
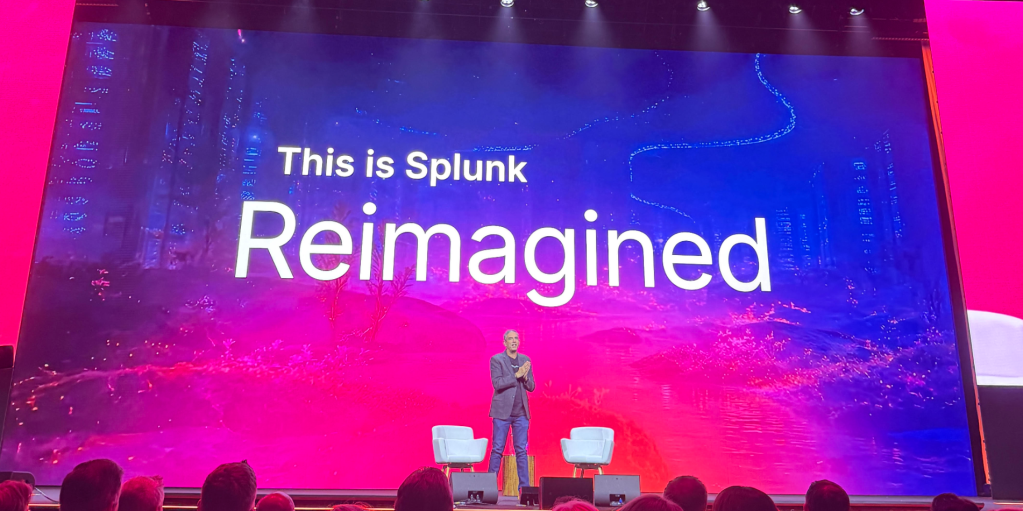
For network engineers, the main takeaway from the Sept.
The short version
- This is an ambitious but badly needed endeavor.
- For years, network teams have been expected to prove whether an incident is “the network,” often while application, cloud, security, and infrastructure teams use different tools and reach competing conclusions.
- The most recent Splunk capabilities aim to replace those fragmented views with a shared operational context, linking network data to application behavior, infrastructure performance, security events, and AI-agent activity.
What happened
Whether it can deliver that unified experience in heterogeneous customer environments will be the test. Network intelligence becomes the centerpiece The most important .conf announcement for network engineers is the new Network Intelligence App for Splunk Observability.
Why it matters
The application will bring Cisco network topology, device health, and event data into Splunk, enabling engineers to trace an alert to the affected device and understand the surrounding network context without leaving the platform.
Summary by Nerd News Network. Read the full article at Network World via the links above and below.