MikroTik patches flaws currently being exploited to take over routers
Networking gear manufacturer MikroTik has released patches for six vulnerabilities in its RouterOS firmware, two of which can be chained together to take over devices without authentication over SSH.
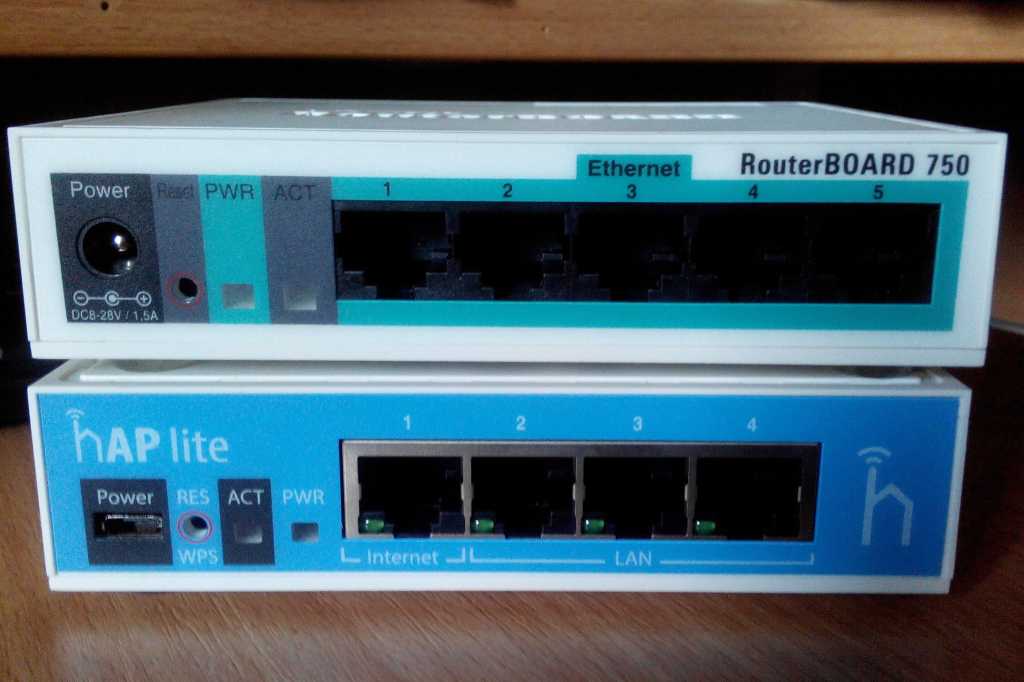
Networking gear manufacturer MikroTik has released patches for six vulnerabilities in its RouterOS firmware, two of which can be chained together to take over devices without authentication over SSH.
The short version
- The exploit chain, dubbed MikroTrick, is already being used by attackers in the wild.
- The vulnerabilities , found by researchers from the CERT Polska, are located in various firmware components, including the SSH server and client, the bandwidth-test service, the X.509 certificate handling code, and the WebFig interface.
- “In recent days we have been observing attacks against RouterOS devices accessible from the internet,” the Polish CERT team said in a report .
What happened
Despite this not being the default configuration, over 122,500 MikroTik devices have SSH reachable from the internet according to scans performed by the Shadowserver Foundation , with the highest numbers in Brazil, the US, and Indonesia. Based in Latvia, MikroTik makes routers, switches, and other networking devices for a wide range of customers, from small businesses to large enterprises.
Why it matters
Its products are used across many sectors, including telecommunications, education, and government.
Summary by Nerd News Network. Read the full article at Network World via the links above and below.